GitHub Copilot Customization Explained for Beginners: Instructions, Prompt Files, Skills, Agents, and Hooks Introduction If you've recently started using GitHub Copilot, you've probably come across terms like Instructions , Prompt Files , Skills , Agents , and Hooks . At first glance, they all seem to do the same thing—they tell Copilot what to do. So why does GitHub have five different customization features? The answer is simple: each feature solves a different problem. Think of GitHub Copilot as a new developer joining your team. On their first day, you don't just hand them code. You explain your coding standards, give them reusable templates, teach them specialized knowledge, assign them a role, and automate repetitive tasks. That's exactly how GitHub Copilot customization works. In this article, you'll learn what each feature does, when to use it, and how they all work together. By the end, you'll know which feature to start with and which ones can wait un...
Azure Container Registry Image Scanning With Azure Security Center
Just to recap in the previous blog post we looked into how to secure Azure Container Registry and in this post will see the offering from Azure Security Center. Azure Container Registry (ACR) is a manged, private container registry service in Azure to build, store, and manage container images and artifacts. ACR service based on the open-source Docker Registry 2.0. This post explains, what you get from Azure Security Center in the context of ACR.


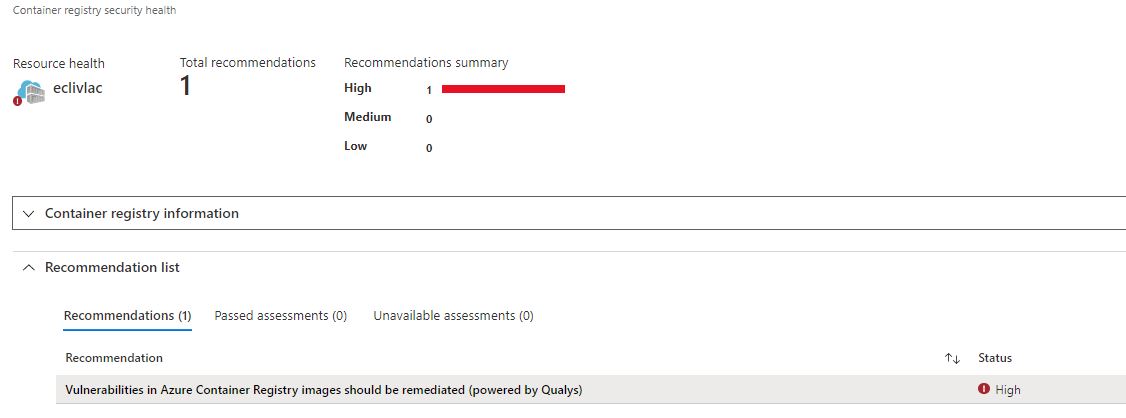

Image scanning is important for any Docker registry. Vulnerability scanning for images stored in Azure Container Registry is now generally available in Azure Security Center (March 2020). This capability is powered by Qualys and seamlessly integrated into the Azure Security Center.
ACR image scanning requires Azure Security Center Standard tier. When you push an image to Container Registry, Security Center automatically scans it, then checks for known vulnerabilities in packages or dependencies defined in the file. Each scan takes approximately 10 min, you will be charged per image scanning operation. Scanned results are shown in Security Center and a security classification for each vulnerability detected, along with guidance on how to remediate issues and protect vulnerable attack surfaces.
Enable ACR Image Scanning
Navigate to Azure Security Center where you can change the pricing tier using the Settings - Pricing Tier blade. Once you have chosen the Standard tier, you can enable the plan for the different resource types in which enable Container Registries for ACR scanning images. Now, all your ACR instances will scan Images and report vulnerabilities, security recommendations to ASC.
Azure Security Center provides dashboards, centralized location related to Security hygiene, Policy & Compliance, Threat protection. For ACR related issues navigate to Security Center - Resource Security Hygiene - Compute & apps, set the filter to Containers, and see all outcomes for services like ACR and AKS.
Recommendations from Azure Security Center
You can click the recommendation to see details about the issues reported.
Under security check findings it shows all the security issues found within images. Clicking on each issue will provide helpful information about the vulnerabilities/security recommendations and learn how to fix it.
Note: At this stage, Qualys’ scanner does not provide any Windows Container image scanning capabilities.
Popular posts from this blog
Automate Certificate Issue and Renewal process - k8s cluster

In this blog post, we will see if you have an existing or new Kubernetes cluster with Ingress resources how do we auto-renew the certificates. If it's not auto-renewed things need to be manually done e.g. every three months you have to renew certificates, delete the expired certificate and secret, update with new certificate secrets accordingly. Manual is always tedious and not an ideal solution especially for your Test & Production environment. Pre-requisites Install and setup kubectl Install and setup Helm Kubernetes cluster already provisioned with Ingress resources. Note: The scope of the blog post is to show how the certificate renewal process can be automated, the same logic can be moved to your Deployment pipelines. Install Cert Manager Installing Cert-Manager CRDs using the below command. #For Kubernetes 1.15+ kubectl apply --validate = false \ -f https://github.com/jetstack/cert-manager/releases/downloa...
Tidy up - Unused Project and Nuget package reference using Visual Studio 2019

If you are a Developer/Architect using Visual Studio as IDE for your development activities, this blog post will be of your interest. During the Ignite 2021 conference, Microsoft released Visual Studio 2019 v16.9 and v16.10 Preview 1. As part of version 16.10 Preview 1, one of the cool features they introduced is to "Remove Unused References..." for any Projects and Nuget packages that are not in use. At the time of writing this blog post, we have Visual Studio Version 16.10.0 (official release) which includes this new feature. As part of development, we generally get carried away and introduce new Nuget package references to your project and add new references to your Projects. By the end of development, you will not be 100% sure which are not being referenced and unused which means you will leave those unused project references in your application. Now you might be wondering what's the big deal in it since it doesn't harm. The advantage of removing unused project r...
Azure App Configuration - How it's different from Azure Key Vault?

Azure App Configuration is a cloud-based managed service that helps developers and infrastructure team members to centralize and manage application configurations and feature flags. Using Azure App Configuration helps to separate application configuration from code. One of the Twelve-Factor App principles states strict separation of config from code with Azure App configuration this can be easily achieved. Azure App Configuration is now generally available as a free or paid service based on the pricing tier you choose as part of provisioning the service. In the modern world, applications often can run in different geographical locations, can be hosted on services like App Services, virtual machines, Serverless functions, Azure Container Instance, AKS, etc. Managing application configuration for all this type of service can be done in a centralized location using App configuration which means your operations and support team members need not...
Comments
Post a Comment